AI System Register
Inventory references, purpose, ownership, lifecycle, provider context, human oversight, internal risk and review dates.
Operational inventoryThe Praesera workspace
Praesera is a private, pre-release desktop workspace for AI governance leads, managers, risk managers, DPOs, internal auditors and consultants. It supports recording AI systems, connecting risks to controls and evidence, documenting assessments and decisions, and following actions over time.
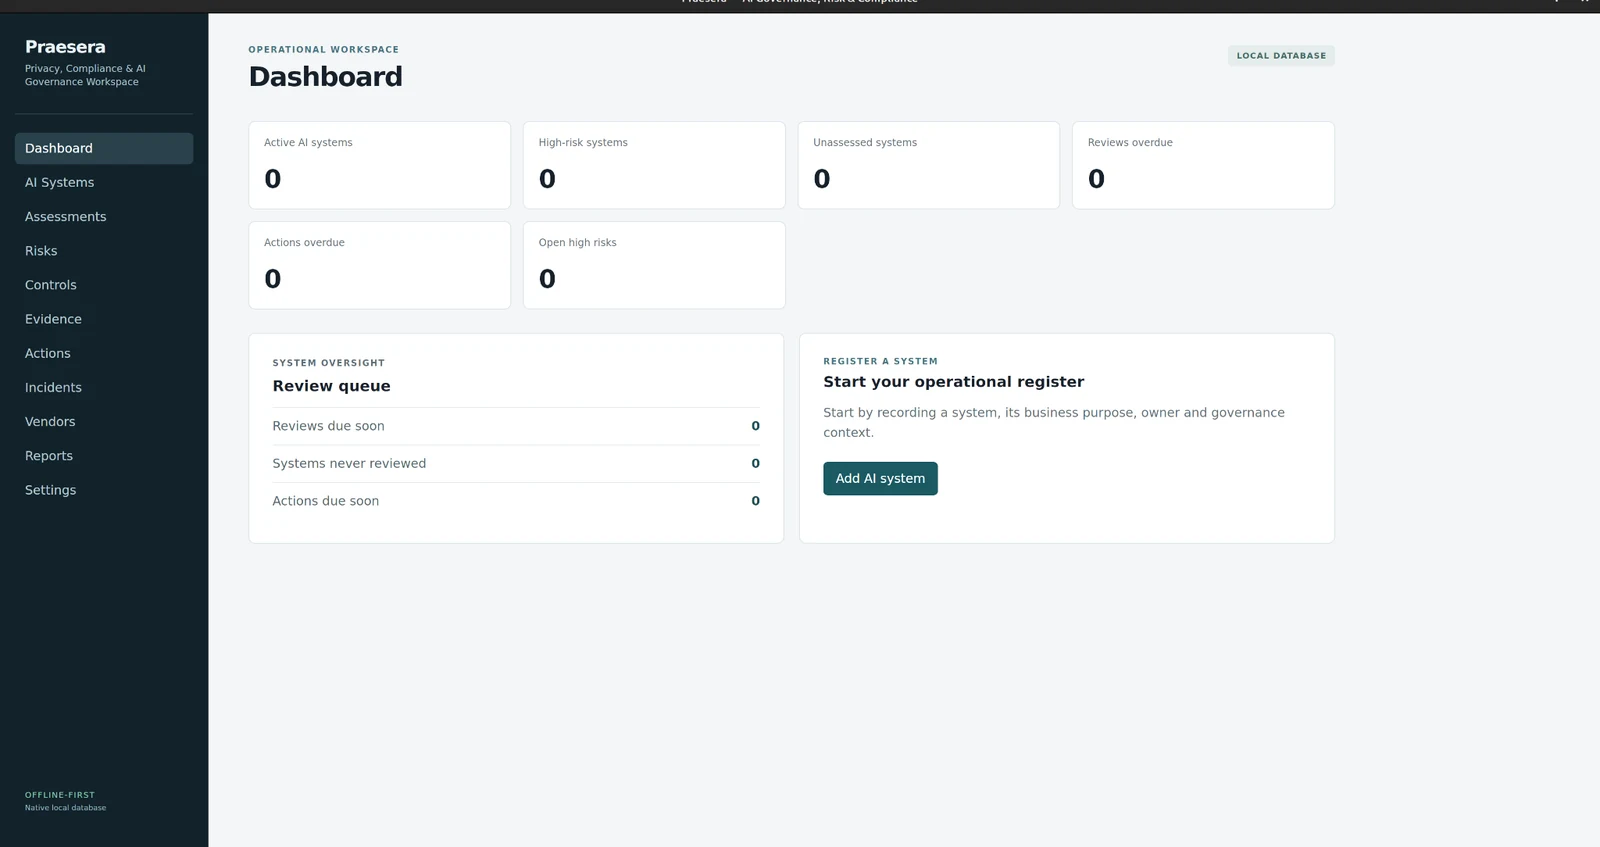
REAL GOVERNANCE WORK SESSION
Praesera begins with an AI system rather than an isolated assessment. Review its purpose, ownership and current governance position, examine the connected risks, controls and evidence, then understand what decisions have already been made and what work still requires attention.
Understand its purpose, ownership and governance context before beginning review.
See linked risks, controls, evidence and assessments together.
Record decisions, assign follow-up and continue the work over time.
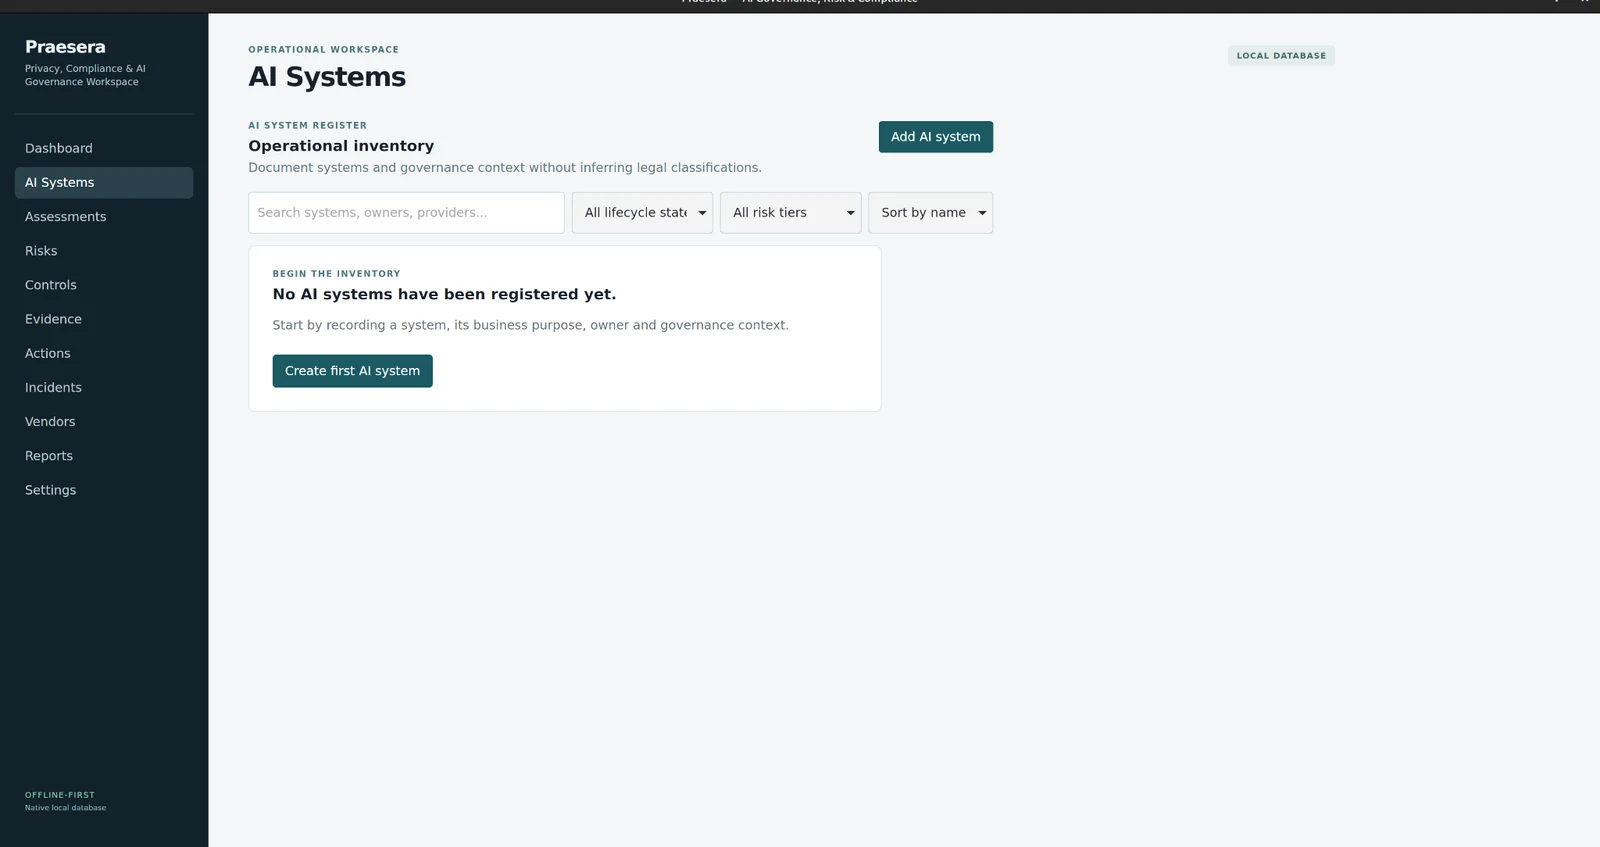
Current product scope
The current workspace brings together systems, assessments, risks, controls, evidence and actions so professionals can review a governance position and follow the work that remains.
Inventory references, purpose, ownership, lifecycle, provider context, human oversight, internal risk and review dates.
Operational inventoryStructured governance review records that can connect back to systems, evidence, actions and future framework requirements.
Assessment foundationInternal qualitative risk analysis, treatment, ownership, residual position and review management without pretending to make a statutory classification.
Internal methodologyImplementation status, operating status, review dates and direct relationships to systems, risks, evidence and actions.
Control lifecycleEvidence metadata, source, custodian, review/expiry state and links to the work that the evidence supports.
Evidence lifecycleRemediation owners, priority, due dates, linked records, completion notes and activity history.
Work queueREAL GOVERNANCE WORK SESSION
Open one AI system and begin with its purpose, ownership and governance context. Review the risks connected to it, examine the controls and evidence that support the current position, then identify what remains unresolved. Praesera keeps the working context together so the next decision and follow-up are clear.
Understand its purpose, ownership and governance context before beginning review.
See linked risks, controls, evidence and assessments together.
Record decisions, assign follow-up and continue the work over time.
Local-first foundation
The current product stores governance records locally and treats storage, migrations, audit history and known limitations as explicit engineering concerns.
Operational records survive application restart and are stored through the Tauri-native persistence layer.
The native data layer maintains schema metadata and migration history rather than silently replacing data.
The user interface depends on domain/repository contracts rather than talking directly to the database.
Encryption, key management, RBAC, managed backup and multi-user architecture will be implemented only when properly designed and tested.
Future framework architecture
Framework mappings are future work. They will be developed against authoritative material with source, version and requirement relationships kept visible rather than inferred automatically.
Future requirement and provenance architecture tied to operational records.
Future relationship between risk-management concepts and organisational governance work.
Future management-system alignment without implying certification.
Future UK-specific guidance and regulatory-source architecture.
Development transparency
Praesera is under active development. The current product scope is shown separately from planned framework support, interface hardening, professional review and broader deployment.
AI System Register, connected Risks, Controls, Evidence and Actions, native local persistence, migrations and audit events.
Improving workspace layout, tables, forms, relationship controls and behaviour across realistic desktop window sizes.
Framework provenance, versioning and requirement relationships, developed deliberately rather than inferred automatically.
Specialist evaluation, Windows QA, packaging, security hardening and future commercial deployment stages.
Praesera Insights
Our working paper examines the operational gap between governance intent and the evidence, controls, responsibilities and actions needed to demonstrate how an AI system is governed in practice.
Free PDF · No registration required
Read the perspectivePraesera
Use the contact link for product, practitioner or future commercial enquiries.